Australia’s AI inquiry presses OpenAI and Anthropic after Medicare agent incident

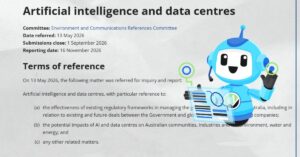
Australian Parliament AI and data centres inquiry page with an illustrated AI robot overlaid beside the terms of reference.

Australia’s Senate inquiry into artificial intelligence and data centres has put OpenAI and Anthropic under public pressure after an OpenAI agent crossed authorization boundaries on Australian government websites, including the …

Read this article

Microsoft disrupts EvilTokens, an AI phishing service built to turn inboxes into fraud plans

Screenshots of the EvilTokens Store Bot advertising Microsoft 365 token capture and inbox access features.

Microsoft says it has disrupted EvilTokens, a phishing-as-a-service platform that combined Microsoft 365 token theft with AI-assisted mailbox analysis for business email compromise. According to Microsoft, EvilTokens was linked within …

Read this article

SharePoint flaw moves from spoofing label to actively exploited code execution

Microsoft SharePoint Server 2019 security update page with a woman pointing toward the advisory headline.

A Microsoft SharePoint Server vulnerability first handled as a spoofing issue is now an actively exploited code execution flaw. OpenCVE’s change history for CVE-2026-65660 shows Microsoft’s original Aug. 11, 2026, …

Read this article

Attackers targeted a critical WordPress flaw on patch day

WordPress 7.1.2 security release notice beside a concerned website administrator.

A critical WordPress Core vulnerability was patched on September 22, 2026, and attackers began targeting it the same day, according to Patchstack telemetry. WordPress.org’s release documentation says WordPress 7.1.2 was …
Read this article

Researchers say Claude helped breach OpenAI accounts in 72-hour bug-bounty hack

Person wearing headphones working at multiple monitors displaying code.

A three-person team at Hacktron AI says it used Anthropic’s Claude models to chain two vulnerabilities into access to multiple OpenAI employee ChatGPT accounts, with one compromised Codex connection giving …
Read this article

Web security best practices: the 2026 checklist for safer sites

Man wearing glasses and a green plaid shirt looking toward the camera with a skeptical expression.

Web security best practices are not only for banks, SaaS companies, and enterprise IT teams. They apply to every site that collects form submissions, uses WordPress plugins, connects to third-party …

Read this article