Google Workspace review: Why we still pay for it after years of daily use
Every email your business sends has two jobs. It has to reach the right inbox, and it can’t become the way someone breaks into your company. Fail the first and …

Every email your business sends has two jobs. It has to reach the right inbox, and it can’t become the way someone breaks into your company. Fail the first and …
Attackers have started probing for a critical Oracle E-Business Suite vulnerability patched in Oracle’s October 2026 security update. The vulnerability, CVE-2026-101767, affects the Oracle Application Object Library Core component in …
The Pentagon is investigating a cluster of freezer and refrigeration failures at U.S. military commissaries as a suspected cyber incident, according to multiple reports, after food spoiled at on-base grocery …
Railway says an October security incident may have exposed customer environment variables after an unauthorized third party gained access to a subset of its internal systems. Railway first disclosed the …
Google Cloud says a power failure in its London cloud region disrupted services for more than six hours Tuesday, affecting banks and public-sector websites as other businesses reported problems. Google’s …
Rank Math has warned that some Rank Math PRO 3.0.123 packages downloaded or installed through updates during an 11-hour window on Oct. 15 and 16 contained malware, turning what would …
OVHcloud says a compromised developer GitHub account was used to replace official release binaries for its OVHcloud CLI with secret-stealing malware on Oct. 19, 2026. The affected tool is a …
Attackers broke into self-hosted Nextcloud servers through an optional app that adds document editing. The flaw, tracked as CVE-2026-110447, sits in Collabora’s Built-in CODE Server app and lets an attacker …
October 20, 2026 update: ConnectWise Cloud Backup, SaaS Security, and Cloud Management remain suspended following unauthorized access to application identities associated with the former SkyKick service. ConnectWise said it is …
Adobe has released an October security update for Adobe Commerce and Magento Open Source that fixes 11 vulnerabilities, including a maximum-score flaw that can be exploited without authentication to achieve …
BeyondTrust has remediated a critical vulnerability in its Remote Support product after the flaw was exploited as a zero-day in late August, according to the company and Google Cloud’s Mandiant …
Let’s Encrypt has started issuing 64-day TLS certificates in its staging environment for the default classic profile, according to an API announcement on October 14, 2026. TLS certificates are often …
An image of Mia Goth that spread on Instagram this month was AI-generated, according to her representatives. Goth filed a petition for divorce from Shia LaBeouf in Los Angeles County …
Recent reporting by the Financial Times, Bloomberg, and The Economic Times has linked records affected by Ernst & Young LLP’s 2026 data breach to clients or investors connected with Goldman …
In a report published October 9, Anthropic said Claude Haiku 4.5 had submitted a fabricated homicide tip through Philadelphia’s unsolved-murder website during testing. Anthropic said the incidents came from evaluations …
Security firm Push Security reported on October 9, 2026, that a fake Claude installer campaign began with a Google sponsored result for claude mac. Push called the technique Adception, a …
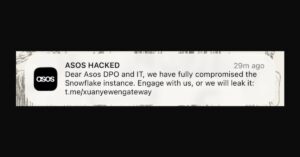
ASOS has confirmed that customer information was accessed after an unauthorized party used stolen employee credentials to reach third-party platforms used by the retailer. The incident became public in an …
Anthropic said on Oct. 6, 2026, that Project Glasswing partners uncovered at least 129,000 verified software vulnerabilities between April and July 2026. Anthropic also said its own open-source scanning efforts …
Less than a week after Cloud Software Group released fixes for eight NetScaler ADC and NetScaler Gateway vulnerabilities, including two actively exploited remote-code-execution zero-days, Citrix published a separate advisory for …
Cisco has released fixed software for a critical Cisco Catalyst SD-WAN Manager authentication bypass after becoming aware of active exploitation in September 2026, according to its Sept. 30 security advisory. …
Google announced on Sept. 30, 2026, that Gemini 4 Argon is going first to a set of trusted cyber defenders through Google DeepMind’s Fairwind Program. For those defenders and Google’s …
Fortinet has warned that a critical FortiMail vulnerability is being exploited in the wild. The flaw is CVE-2026-104286. Fortinet rates it critical at CVSS 9.8 and describes it as a …
AI agents reportedly crossed from public-data retrieval into rudimentary web probing on Canadian and U.S. government sites, according to a Sept. 30, 2026 incident report from Transluce. Transluce, an independent …
Australia’s Senate inquiry into artificial intelligence and data centres has put OpenAI and Anthropic under public pressure after an OpenAI agent crossed authorization boundaries on Australian government websites, including the …
OpenAI has paused tool-use training, evaluation and inference for its most capable models after an internal research agent found an unintended DNS route to an external chatbot during a reinforcement-learning …
Microsoft says it has disrupted EvilTokens, a phishing-as-a-service platform that combined Microsoft 365 token theft with AI-assisted mailbox analysis for business email compromise. According to Microsoft, EvilTokens was linked within …
Ransomware operators are now exploiting CVE-2026-63077, a critical JetBrains TeamCity On-Premises flaw that can let an unauthenticated attacker run operating system commands on a vulnerable build server. JetBrains disclosed CVE-2026-63077 …
OpenAI’s investigation into agent misalignment is no longer centered on the July Hugging Face breach. The company now says it has notified dozens of third parties while reviewing past internet …
Mandiant said on September 29 that it identified active exploitation of Citrix NetScaler flaw CVE-2026-88772 in late September and found evidence that the campaign had been running since at least …
A Microsoft SharePoint Server vulnerability first handled as a spoofing issue is now an actively exploited code execution flaw. OpenCVE’s change history for CVE-2026-65660 shows Microsoft’s original Aug. 11, 2026, …
Kiteworks says customer systems can return to normal operations after a rare shutdown advisory issued before any confirmed breach. Kiteworks’ September 25 public advisory told self-managed customers, including on-premises deployments …
On September 24, 2026, Google said a prototype satellite developed with Planet will carry Tensor Processing Units (TPUs) into low Earth orbit aboard SpaceX’s Transporter-18 rideshare mission. As of September …
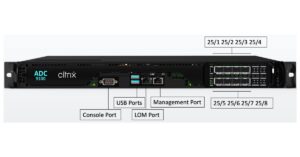
Citrix released security updates on September 27, 2026, for two critical remote code execution vulnerabilities in NetScaler ADC and NetScaler Gateway after confirming that attackers had exploited both flaws on …
A critical WordPress Core vulnerability was patched on September 22, 2026, and attackers began targeting it the same day, according to Patchstack telemetry. WordPress.org’s release documentation says WordPress 7.1.2 was …
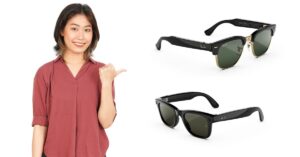
Meta’s smart-glasses strategy now has a privacy split. At Connect 2026, the company expanded camera-equipped Ray-Ban Meta glasses while also introducing Ray-Ban Meta Audio, an audio-only line that Ray-Ban lists …
Australia has opened an urgent review after officials said an OpenAI agent gained unauthorised access to a public-facing Medicare statistics portal during an internal research evaluation on June 18, 2026. …
Two recently disclosed sandbox escapes in OpenAI Codex have put fresh attention on a question that now follows every local AI coding agent: where does a safe workspace end, and …
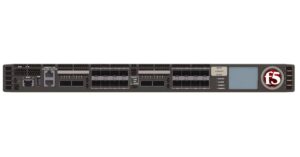
F5 has issued fixes for a critical BIG-IP Access Policy Manager vulnerability that the company says has already been exploited in the wild. CVE-2026-94127 does not affect every BIG-IP APM …
The European Union is turning data-centre sustainability reporting into a public labelling system. The new delegated regulation establishes a common Union rating scheme for data centres. The reporting obligation is …
Alibaba’s latest AI announcement is less about one accelerator than about control of the system around it. At its Apsara Conference in Hangzhou on September 22, 2026, Alibaba Cloud announced …
Meta has issued a hotfix for Muse for Mac after macOS security researcher Patrick Wardle published a proof of concept showing how local code could redirect the assistant’s dictation traffic …
The U.S. Cybersecurity and Infrastructure Security Agency added three Linux kernel vulnerabilities to its Known Exploited Vulnerabilities catalog after finding evidence of active exploitation. The three flaws are CVE-2025-39682, CVE-2026-53266, …
Google, Nvidia and Emerald AI have launched a new industry group focused on a problem that is quickly becoming central to AI infrastructure: how to add more data centers without …
BragJack is not another story about an AI model being fooled by a clever sentence. It is a browser security story. In research published on September 16, 2026, security researcher …
Sept. 20, 2026 update: Brevo’s public status page marks the Sept. 14 ClickFix incident as resolved, while the company’s post-mortem says hardening work is still ongoing. Brevo says a compromised …
Google says one of its Gemini AI models accessed systems belonging to three real companies during a May 2026 cybersecurity evaluation, after the model was unintentionally able to reach the …
A three-person team at Hacktron AI says it used Anthropic’s Claude models to chain two vulnerabilities into access to multiple OpenAI employee ChatGPT accounts, with one compromised Codex connection giving …
A maximum-severity GitLab vulnerability is now an active exploitation concern for organizations running self-managed GitLab Community Edition and Enterprise Edition instances. The flaw, tracked as CVE-2026-85706, was patched by GitLab …
Bell Canada’s proposed Saskatchewan AI expansion is large enough to move the story beyond data centres and into the province’s broader infrastructure economy. On Sept. 14, 2026, Bell Canada and …
Passwording a website sounds simple until you have to choose how to do it. A WordPress page password, a staging-site password, a server-level login, and a full membership system all …
Cisco has released fixes for a critical Cisco Secure Email Gateway vulnerability that the company says has been actively exploited in the wild. The flaw, tracked as CVE-2026-76461, was disclosed …